
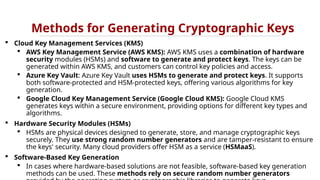
The Place the worth of the data demands it, keys ought to be encrypted whenever saved and only be made available in unencrypted form inside a safe, tamper-protected setting and even (in excessive cases) kept offline. Pomerium accepts documented certificate, signing, shared-secret, and service-account configuration. Operators own era, custody, entry, distribution, stock, rotation, revocation, recovery, and destruction. Pomerium cannot invalidate an exterior key or discover copies outside its configured deployment. CSA’s Cloud Key Management Foundations course is predicated on our cloud key administration research initiatives and associated artifacts.
Perform Regular Audits And Keep Compliance
Hash capabilities create a small, fixed-length digest worth (known as the hash value) from a usually larger value that may be of arbitrary dimension. By converting the initial enter worth right into a extra compressed worth, hash features are an environment friendly and safe mechanism for guaranteeing knowledge integrity in asymmetric encryption. Nonetheless, since hashing is a one-way process with no idea of a key or decryption routine, preliminary input values can’t be decrypted and accessed after being hashed. By No Means escrow keys used for performing digital signatures, but consider the want to escrow keys that assist encryption.
Distribution, Use, And Rotation
Get monthly insights on certificate management, post-quantum readiness, and enterprise safety. Monthly insights on certificates management, post-quantum readiness, and enterprise safety. Keys must not ever exist in plaintext exterior a secure boundary.A key in a config file, setting variable, supply code, or email is a compromised key. Distribute keys solely through authenticated, protected channels to named customers. Keep Away From supply code, container images, command strains, logs, general https://patrickobrienfoundation.org/heres-what-you-must-know-about-social-security-disability-insurance-law/ configuration, and unrestricted surroundings variables.
Key Administration For Large-scale Enterprises
Bind each operation to an authenticated workload and an authorization coverage. When a secret is compromised, all use of the vital thing ought to stop, and the compromised key should be revoked. Sturdy cryptographic techniques may be compromised by lax and inappropriate human actions. Highly uncommon events must be famous and reviewed as attainable indicators of tried assaults on the system. Hardware cryptographic modules are preferred over software program cryptographic modules for defense. Over the following decade businesses might want to begin utilizing “post-quantum cryptography” algorithms as permitted by NIST.

- Whereas different KMS choices present varying capabilities and features, they sometimes leverage widespread, foundational components to achieve optimum key administration.
- Key storage determines how and where private keys are positioned.
- Using robust cryptographic protocols corresponding to SSL/TLS helps safe communication channels throughout key change, lowering the chance of interception or unauthorized entry.
- The evidence means that there was a weather report broadcast over radio which would have warned the tug-captains of the climate and persuaded them to put into harbor.
Key distribution can present many challenges, together with safety dangers that would leave both parties weak to interception. Collectively, cryptographic algorithms and keys allow robust security and privacy in a broad range of use instances, from securing person authentication processes and website site visitors to signing digital signatures and encrypting data-at-rest. While totally different KMS offerings present various capabilities and options, they sometimes leverage common, foundational elements to achieve optimum key management. This weblog, derived from CSA’s lately released cloud key administration Cloud Infrastructure Security course, discusses cryptographic keys and algorithms and the differences between the kinds of encryption they offer. You can dive deeper into cloud key administration by signing up for the course right here. If key owners, developers, or system maintainers suspect a key compromise, they should promptly rotate the affected keys and re-encrypt any data that was secured with the compromised keys.